How Can AI Agents Read Untrusted Sources Safely?
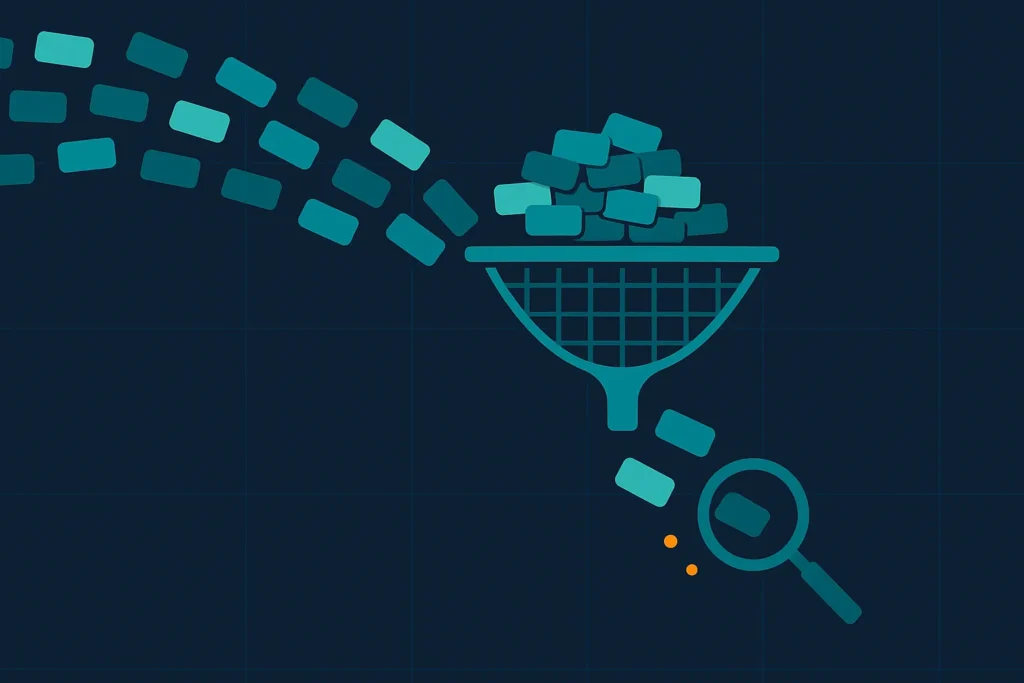
AI adoption’s main villain is safety. We’ve been seeing incidents of data exfiltration and confused deputy attacks. It happens because an LLM is probably the weakest link in the system. Most attacks happen when AI agents are exposed to the lethal trifecta. If agents can read from untrusted sources, access internal knowledge, and communicate to …
How Can AI Agents Read Untrusted Sources Safely? Read More »